Continuous Compliance vs. Point-in-Time Audit Preparation

Updated: Sep 30
Author: Ashwin Kondapalli, Founder & CTO, LoopIQ Updated: September 30, 2026
Continuous compliance in software delivery means capturing approvals, tests, changes, and exceptions as work happens so evidence stays review-ready—unlike point-in-time audit prep, which rebuilds proof under a deadline.
Two weeks before the audit, a compliance lead opens a shared folder labeled "Evidence Q3." Half the links are stale. Approvals live in email. Test exports do not name the build that shipped. Someone asks engineering to "just pull everything for last quarter's releases." The team ships every week. Nobody can reconstruct why any single release was considered ready.
That scramble is point-in-time audit preparation. The alternative—continuous compliance in software delivery—is not constant external audits. It is keeping control evidence current as work happens so a release review or audit request is a report on an ongoing state, not a fire drill.
This guide compares the two practices, explains why the release is the right evidence unit for delivery teams, and shows how a connected Release Compliance Dossier supports readiness decisions without promising guaranteed audit outcomes.
What is continuous compliance in software delivery?
Continuous compliance in software delivery is the practice of capturing and connecting control evidence—approvals, changes, test results, exceptions, access and operational signals—as delivery work happens, so release readiness and audit review start from a current package rather than reconstructed notes.
In plain terms:
Controls operate as part of delivery (recorded approvals, linked tests, managed change).
Evidence is captured at or near the source when the event occurs.
Drift and gaps are visible while there is still time to fix them.
Per-release evidence can be reviewed on demand—not only in "audit week."
Continuous compliance is a practice, not a permanent badge of being "compliant." Being compliant is a state relative to policies and frameworks; continuous compliance is how you keep evidence reviewable without bursts of manual prep.
It does not mean:
Constant external audits.
Automatic regulatory certification.
That passing tests authorize a release.
Guaranteed zero findings or "100% compliant" status.
LoopIQ release certifications are internal governance records that support readiness and audit review. They are not external regulatory certificates.
What is point-in-time audit preparation?
Point-in-time audit preparation is episodic evidence assembly: teams pause or divert delivery work to gather screenshots, exports, ticket comments, and spreadsheet summaries for a defined period, then return to normal until the next review.
Typical pattern:
Audit or customer questionnaire is scheduled.
Owners chase artifacts across tools and chat.
Evidence is copied into a binder, folder, or GRC upload.
Findings appear where linkage or freshness was never maintained.
The binder ages; the next cycle starts from near-zero again.
Point-in-time prep is sometimes unavoidable—new frameworks, first audits, or gaps in tooling. The problem is treating it as the only model while release velocity and overlapping controls keep rising. Manual reconstruction cannot keep pace with frequent ships, AI-assisted change, and auditors who expect connected evidence from intent through deployment rather than a one-time snapshot.
Side-by-side: continuous evidence vs periodic prep
Comparison:
Timing — Evidence captured as work happens — Evidence assembled under deadline
Unit of review — Often per release / change / control event — Often per quarter, year, or engagement
Primary question — "Why was this release considered ready?" — "Can we prove controls for this period?"
Failure mode — Incomplete linkage or stale signals — Missing artifacts and contradictory exports
Effort shape — Steady hygiene + automated capture — Spikes of reconstruction labor
Release go/no-go — Can reuse the same package — Often separate from audit folders
After the review — Evidence stays attached to the work — Binder may not update with new releases
Neither column replaces auditors, legal counsel, or framework-specific controls. Continuous capture feeds periodic reviews; it does not erase the need for human judgment, exception handling, or external assessment where required.
Illustrative contrast (demo data—not a customer result):
Release billing-ui 2026.09.12 — Point-in-time: chase PR approvals and selenium later — Continuous: dossier already lists linked change requests, approval timestamps, test executions on build sha-9f3c, and one dated exception
Open high finding — Point-in-time: discovered in audit binder as unaddressed — Continuous: dispositioned at release review with owner, expiry, and rationale
Why release evidence is the right unit of continuous compliance
For software delivery organizations, the release (or equivalent change window) is where risk concentrates: scope, approvals, tests, security signals, and operational readiness meet in one decision.
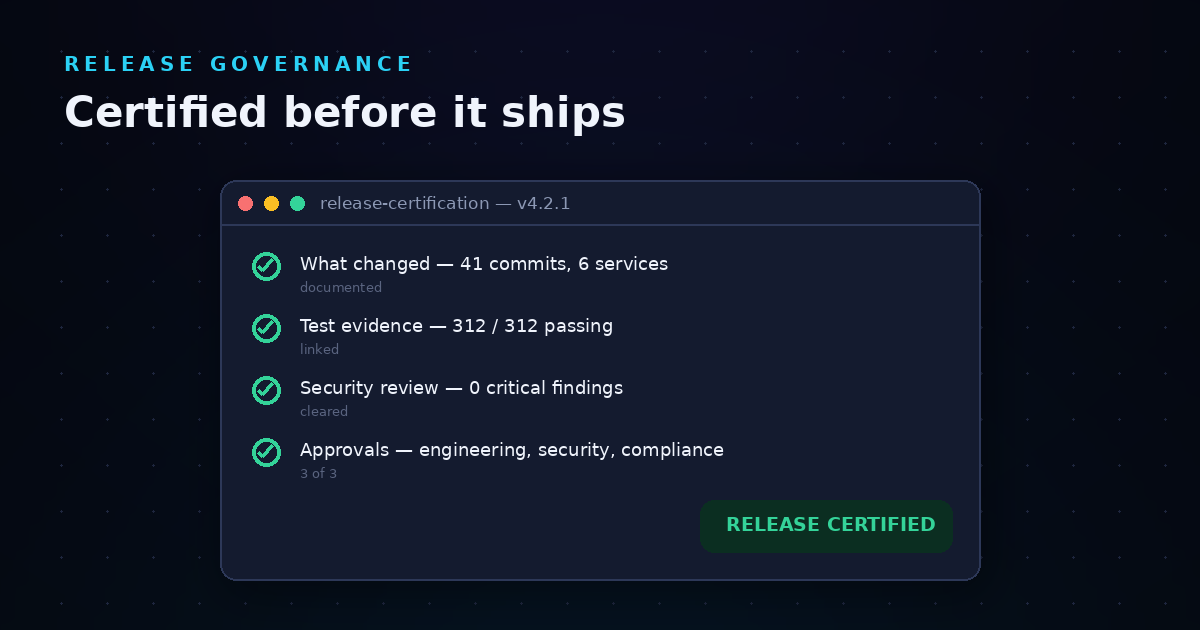
A Release Compliance Dossier is a connected evidence package for a release. It helps answer: why was this release considered ready, and what evidence supports that decision?
Depending on how your organization uses LoopIQ, a dossier may include:
Release details and related change requests
Linked stories, tasks, issues, and defects
Approval history and release certification decisions
Test plans, cases, executions, and results
Exceptions, deviations, and risk notes
Linked documents
Integration signals from source control, CI/CD, security scanning, or observability tools
Final readiness notes and decision history
Without a connected dossier, teams rebuild that package from chat messages, ticket comments, spreadsheets, and document folders—exactly the point-in-time pattern.
Release certification in this context means recording a traceable readiness decision path inside your governance process. It is not the same as regulatory certification by an external body. Passing tests remain inputs to readiness; they do not alone authorize release.
Organizations that also use GRC posture tools still need delivery-side evidence that maps to what shipped. Continuous release packages reduce the copy-paste gap between engineering systems and audit uploads. Do not treat any product as a guaranteed audit outcome.
How this works in LoopIQ
LoopIQ connects delivery work, testing, AI agents, and operational signals so teams can assess release readiness, control changes, and preserve the evidence behind their decisions—shifting effort from periodic reconstruction toward ongoing dossier hygiene.
Prerequisites
Releases exist in LoopIQ and related work items are linked where possible.
Required test records have been created or imported.
Approval policies are configured if your process requires them.
Exceptions or deviations are recorded when standards are not fully met.
Sequence (continuous capture → reviewable package)
Keep work items, changes, and tests linked to the correct release early—not the week before an audit.
Open the release or release certification record.
Review linked work, change requests, and approvals.
Review test evidence and quality signals against the intended build.
Review open exceptions, deviations, or known risks; add missing evidence or comments.
Use the dossier during release review and when audit preparation needs a per-release package.
Approvals and outputs
Certification records track pending, approved, or declined decisions.
The dossier remains a governance record for readiness and audit review—not an external certificate.
Automation rules can request approvals or enforce required fields; human approval and viewing existing results remain part of normal workflow. Confirm credit and charging rules for certification generation in your deployment (pricing: paid platform $4.99/user/month; chargeable operations defined separately).
Atlassian note: Atlassian synchronization is supported for Jira, Jira Service Management, Confluence, Compass, Bitbucket, and Assets through a provider-neutral external-resource model, with native LoopIQ project management and ITSM available in connected or hybrid modes. See current product notes. Capability depends on connection and mapping configuration—do not assume identical real-time sync for every object.
Good dossier hygiene (from product guidance): Link early. Avoid comments as the only evidence when a structured field or linked record exists. Keep exceptions explicit. Confirm test results are complete before approving readiness.
Practical first steps (without boiling the ocean)
You do not need to "finish compliance" before improving capture. Start where reconstruction hurts most:
Pick one release train and require linked work + named decision owner for go/no-go.
Define "enough evidence" for that train: approvals, test baseline, security freshness, exception rules.
Record exceptions with expiry and approver—silent deferrals are future audit findings.
Review one dossier end-to-end before the next ship; list gaps with owners.
Only then widen to more teams or connect additional signal sources.
If you are still in pure point-in-time mode, use the next audit as a forcing function: every artifact you chase should become a standing linkage or field on the next release—not another orphan file in "Evidence Q4."
Common misconceptions
"Continuous compliance means constant audits." No. It means always-current, reviewable evidence. External audits remain scheduled events; preparation should not require rebuilding history from scratch.
"It replaces audits." No. It makes audits and customer reviews less disruptive by keeping evidence attached to delivery work. External assessment and legal obligations remain.
"Green pipelines equal continuous compliance." No. Pipelines are one signal. Approvals, scope, exceptions, operational readiness, and recorded decisions still matter. Passing tests do not authorize a release.
"It requires more manual work." Done poorly (duplicate binders plus live systems), yes. Done as source capture and release packages, it usually reduces audit-week spikes. It is not zero-maintenance.
"One tool makes us fully compliant." No vendor should claim "100% compliant," flawless evidence, or guaranteed audit outcomes. Tools preserve and connect evidence; organizations own policy, judgment, and formal certifications where required.
"Continuous compliance is only for large companies." Any team with recurring audits or customer security reviews benefits from not reconstructing releases after the fact—regardless of headcount.
FAQ
What is continuous compliance in software delivery?
Continuous compliance means capturing approvals, tests, changes, and exceptions as delivery happens so evidence stays review-ready. It is not constant external audits.
How is that different from point-in-time audit preparation?
Point-in-time prep rebuilds proof under an audit deadline from folders, email, and exports. Continuous compliance keeps that proof attached to releases so reviews report on an ongoing state.
Does continuous compliance replace audits?
No. External audits and customer reviews still happen on a schedule. Continuous capture makes them less disruptive because you are not reconstructing last quarter from scratch.
Do green pipelines equal continuous compliance?
No. Pipelines are one signal. Approvals, scope, exceptions, operational readiness, and a release dossier are part of the evidence story tests alone cannot finish.
Can a tool make a team fully compliant?
No vendor should claim guaranteed audit outcomes or flawless evidence. Tools help connect work, controls, and evidence; humans still own decisions and regulatory obligations.
See a release evidence review in LoopIQ
If audit week still means reconstructing last quarter's releases from chat and exports, shift the unit of work to per-release evidence: checklist domains at go/no-go, a maintained dossier, and an explicit readiness decision.
CTA: See a release evidence review in LoopIQ. Book a time: https://meet.brevo.com/ashwin-kondapalli
Further reading:
This article consolidates and replaces the thinner "What Is Continuous Compliance in Software Delivery" explainer on the same URL. General information for engineering, quality, release, and compliance leaders. Not legal, audit, or regulatory advice.
(Product screenshot to be added.)